Your servers under our watch
Patched before the next alert, with a report every month. We take over the security of the servers your site or service runs on. Any stack, from $290 a month.
- A patch window on an agreed day
- Security alerts watched for your stack
- Holes used in attacks fixed within one business day
- A report on what was updated
New holes every month, and nobody on your servers
Attackers move faster than updates
The PHP2Shell flaws were fixed on 21 October 2026. Five days later, CISA added them to its list of vulnerabilities already used in attacks.
Nobody owns the servers
The developer who set them up has moved on. Your hosting does not update what runs on your server. And the version on the screen often stays the same after a fix, so you cannot tell what is closed.
What a missed fix costs
A stranger's page instead of your site, a Google warning in front of your customers, and leads that never reach you.
A site that was left alone
A former client, no longer on our support
On 20 October 2026 we found attackers' pages on the site of a former client that was no longer on our support. By mid November the owner had replaced the whole site with a placeholder. Nobody was watching its server.
We take over the security of your servers
Not only PHP. Whatever runs on your servers, we keep it patched and watched, every month.
A starting audit
Three business days. Access, a full list of what runs on your servers, a backup, missing fixes, unsupported versions and signs of a break-in, then the first patch window and a starting report.
A monthly patch window
On an agreed day we install the updates, restart the services one by one and check your pages, forms and admin.
A watch on security alerts
Between windows we follow the security alerts for the exact versions you run.
A fast fix for a critical hole
A critical fix does not wait for the window. A hole already used in attacks is fixed within one business day after the fix comes out, any other critical hole within three business days. Then we confirm the hole is closed.
A monthly report
What we updated, what we checked and what needs your decision, in plain words.
Any stack
nginx or Apache, PHP, Java, Node.js, Python, Docker images, WordPress and custom code.
We already do this for our clients
20 clients, 23 domains checked
When the PHP2Shell flaws came out, we checked every PHP site we have built: 20 clients, 23 domains. When a critical vulnerability comes out, we check the servers, install the fixes and confirm the hole is closed.
What you get
Patched before the next alert, not after a break-in
One team answers for the security of your servers, so you do not have to think about it.
- Your servers patched before the next alert
- A monthly report you can forward to a partner or your accountant
- Your site keeps working: every update with a backup and a check
- One team that answers for the security of your servers
If we miss a fix, the repair is on us
We fix it or restore it at no cost
If your site goes down or gets broken into through a hole we should have closed, we fix it or restore it from the backup at no cost.
One monthly plan
From $290 a month
For one site and the server it runs on. Each next site or server adds $190 a month. The starting audit is $350 once, free when you pay three months ahead. The contract runs from three months. For comparison, one emergency PHP upgrade with us costs $490 per site.
- Starting audit ($350 value), free with three months ahead
- Monthly patch window
- Watch on security alerts
- Critical fixes within one to three business days
- Monthly report
- The repair on us if we miss a fix
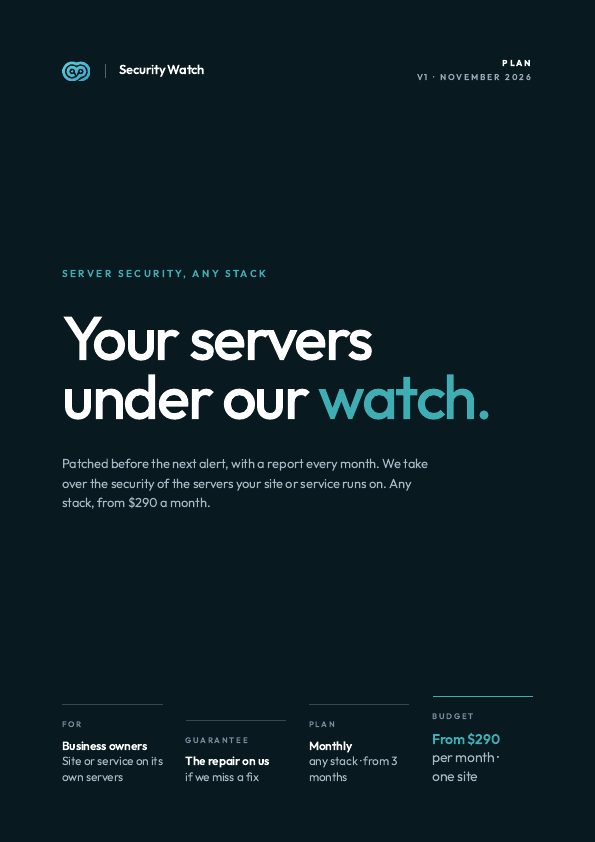
Download the Security Watch plan
Six pages: why it matters, what we do every month, the price, the terms and the common questions. Easy to forward to a partner or your team.
Download the plan (PDF)PDF, 6 pages, 0.4 MBFrom your site address to a monthly watch
Send us your site address
We look at it from the outside for free and tell you what we see.
The starting audit
Three business days: a full picture of your servers, the first patch window and a starting report.
Every month
Updates in the window, a watch on alerts between windows, and a report at the end of the month.
Questions we hear
Critical holes now come out every few days. A monthly window keeps the regular updates in order, and the watch catches the critical ones in between.
Any stack on Linux servers: nginx or Apache, PHP, Java, Node.js, Python, Docker images, WordPress and custom code. The starting audit lists everything that runs there.
If your site goes down or gets broken into through a hole we should have closed, we fix it or restore it from the backup at no cost. The guarantee covers the repair and the restore, not lost sales.
Moving to a new major version, for example from an old PHP that no longer gets fixes, and cleaning up a server that was broken into before we took it over. We price them separately after the starting audit.
Yes, from three months. The starting audit is $350 once, and it is free when you pay the first three months ahead.
We check the fixed package from the vendor or your Linux distribution, not only the version number. Distributions often ship a fix without changing that number. The monthly report lists what we checked.
We install updates in the agreed window and restart the services one by one, then check that the site works. If an update needs downtime, we tell you before.
Yes. Send us your site or server address. We look at it from the outside today and tell you what needs fixing.
One team for the whole system
Tell us what runs on your servers
Send us your site or server address and what runs there. We'll reply with what needs fixing first and what the monthly plan would cost.
- A free first look at your site
- The number named before you pay
- NDA on request
- [email protected]Vitaliy, CEO
- Tallinn, EstoniaOwlab OÜ, legal address
- Ukraine and the EUOur team
 Vitaliy AntoshchenkoFounder and CEO, Owlab
I reply myself with what needs fixing first.
My AI assistant or a short form. About a minute.